The ongoing conflict between Ukraine and the Russian Federation has officially expanded deeper into the digital domain, marked by a coordinated wave of cyber intrusions targeting national early-warning infrastructure. Late on Sunday, official air raid and civil defense warning applications in both warring nations were simultaneously compromised by unknown threat actors. The cyberattacks successfully injected false, highly alarming notifications into the smartphones of millions of citizens. These fabricated alerts falsely warned populations of catastrophic events, including imminent nuclear strikes, chemical weapon deployments, and active street combat.
The security breaches have not only exposed profound vulnerabilities in the public safety architectures of both countries but have also amplified the psychological toll of a war that has persisted for years. While cybersecurity experts and government officials scramble to identify the perpetrators, the simultaneous nature of the breaches has ignited intense speculation regarding the involvement of sophisticated state-sponsored advanced persistent threat (APT) groups, rogue insider factions, or independent hacktivist collectives seeking to sow chaos and panic among civilian populations.
Chronology of the Incident: A Sunday Night of Digital Panic
The sequence of events began unfolding on Sunday evening, catching millions of civilians off guard in both Kyiv and Moscow. The timeline of the breaches highlights a coordinated effort to destabilize the home fronts of both nations within hours of each other.
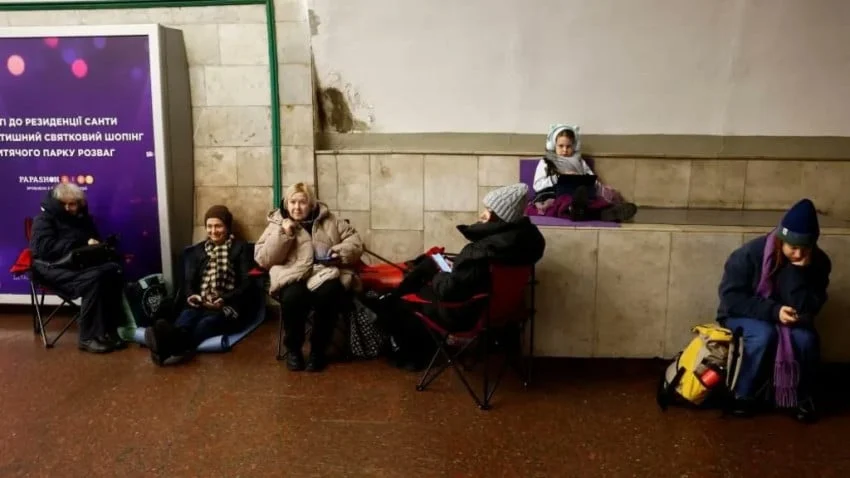
At approximately 8:30 PM local time in Ukraine, users of the widely adopted "Air Alarm" smartphone application—an essential tool downloaded by millions to survive regular aerial bombardment—began receiving unprecedented notifications. Instead of the standard localized alerts signaling incoming Russian drones or cruise missiles, the application triggered a nationwide "red-level" air raid warning. Compounding the terror, secondary alerts were pushed to residents in specific strategic zones, including the capital city of Kyiv, warning of immediate radiological hazards, chemical warfare threats, and active urban warfare.
For a population that has grown accustomed to the terrifying rhythm of nightly air raids, the inclusion of nuclear and chemical warnings marked an alarming escalation. Panic briefly surged across social media platforms as citizens tried to verify the validity of the alerts. However, discerning users quickly noted linguistic anomalies: the false notifications were composed in Russian rather than Ukrainian, immediately raising suspicions of external manipulation.
Within hours, as the digital dust began to settle in Kyiv, a parallel incident unfolded across the border in the Russian Federation. Late Sunday night, authorities in Moscow reported that equivalent regional civil defense and air alert systems had also been successfully breached. Much like their Ukrainian counterparts, Russian users received unauthorized emergency messages. However, instead of systematic strategic warnings, the Russian breaches featured erratic, sometimes profane language designed to mock civil defense protocols and rattle the local population.
Anatomy of the Breach: Technical Vulnerabilities and Official Responses
As daylight broke on Monday, cybersecurity agencies and governmental bodies in both Kyiv and Moscow issued damage-control statements, attempting to calm jittery populations and clarify the extent of the digital incursions.
In Ukraine, the Air Force and the Ministry of Digital Transformation moved swiftly to counter the psychological impact of the hack. In an official statement distributed via their secure Telegram channels, the Ukrainian Air Force declared: "The Air Alarm application may have been subjected to enemy interference. There is no radiation threat! Remain calm and follow our updates on our official channel."
Engineers and developers behind the application temporarily disabled the service for emergency maintenance, locking down servers to conduct forensic audits. Preliminary technical assessments indicated that the attackers likely leveraged compromised third-party notification pipeline credentials or exploited vulnerabilities in the cloud-based messaging architecture utilized by the app developers. Because modern early-warning applications rely heavily on rapid, cloud-based push notification services to bypass delivery delays, they remain vulnerable to supply-chain attacks if an intermediary server is compromised.
Meanwhile, Russian authorities faced a similar administrative nightmare. Regional emergency ministries in several Russian oblasts acknowledged that their public warning portals and mobile applications had been manipulated by unauthorized actors. While Russian state media downplayed the operational impact of the hack, emphasizing that critical military command-and-control networks remained entirely isolated and secure, the breach of civilian-facing apps represented a severe public relations embarrassment for a regime that prides itself on strict information control and robust cybersecurity defenses.
Attribution and the Fog of Cyber War
To date, no specific state actor, hacktivist collective, or individual has claimed responsibility for the dual cyberattacks. The obscurity surrounding the attribution has fueled a myriad of geopolitical theories among international cybersecurity analysts.
The primary question baffling investigators is whether the simultaneous breaches were the result of a single, highly capable actor executing a symmetrical false-flag operation, or two entirely independent entities striking opposing sides on the same evening.
If the attack originated from a single sophisticated APT group, the motive may have been psychological experimentation—testing the limits of public panic and evaluating the speed at which national infrastructures can recover from a coordinated psychological operations (PSYOP) campaign. Alternatively, the breach could be the handiwork of decentralized hacktivist networks, such as pro-Ukrainian groups targeting Russian infrastructure, met with a retaliatory or opportunistic counter-hack by pro-Russian cyber militias against Ukrainian public applications.
Intelligence analysts note that targeting civilian warning systems violates traditional norms of armed conflict, which generally delineate between military targets and civilian infrastructure. However, as the boundaries of modern hybrid warfare continue to blur, the digital home front has transformed into a primary theater of operations.
Broader Implications for Civilian Safety and Digital Resilience
The events of Sunday night carry profound implications for the future of civil defense, urban resilience, and public trust in emergency communications technology during times of war.
First and foremost, the attacks highlight the dangerous fragility of smart-device early-warning systems. While applications like Ukraine’s Air Alarm have saved countless lives by providing precious minutes of advanced notice before missile impacts, their reliance on commercial telecommunications networks and centralized cloud servers makes them attractive targets for malicious actors. When citizens can no longer trust the authenticity of an emergency alert, the entire architecture of civil defense begins to crumble. Hesitation born from skepticism during a genuine nuclear, chemical, or conventional attack could result in catastrophic loss of life.
In the wake of the incident, Ukrainian officials reiterated guidance instructing citizens to cross-reference emergency alerts with independent verification channels, such as official state Telegram broadcasts, radio transmissions, and siren networks, rather than relying exclusively on a single smartphone application.
Furthermore, the incident forces a reassessment of cybersecurity protocols among the private tech contractors who frequently partner with governments to build and maintain public safety infrastructure. Moving forward, developers of civil defense software will likely face stringent regulatory mandates to implement multi-factor authentication, end-to-end encryption for push notifications, and isolated, air-gapped backup systems that cannot be easily penetrated via external cloud vectors.
Conclusion
The simultaneous hacking of air raid and nuclear warning applications in Ukraine and Russia marks a chilling milestone in the evolution of modern cyber warfare. By weaponizing fear and turning civilian safety applications into vectors for psychological manipulation, the unknown perpetrators have demonstrated the acute vulnerability of the digital home front. As the physical war grinds on across blood-soaked trenches and contested skies, the invisible war within the servers and smartphones of millions continues to escalate, proving that no sanctuary—not even the digital notification screen—remains untouched by the conflict.
